What is true today
eFind Pay is in development. The current website does not open a bank account, hold funds, transmit money or process live eFind Pay transactions.
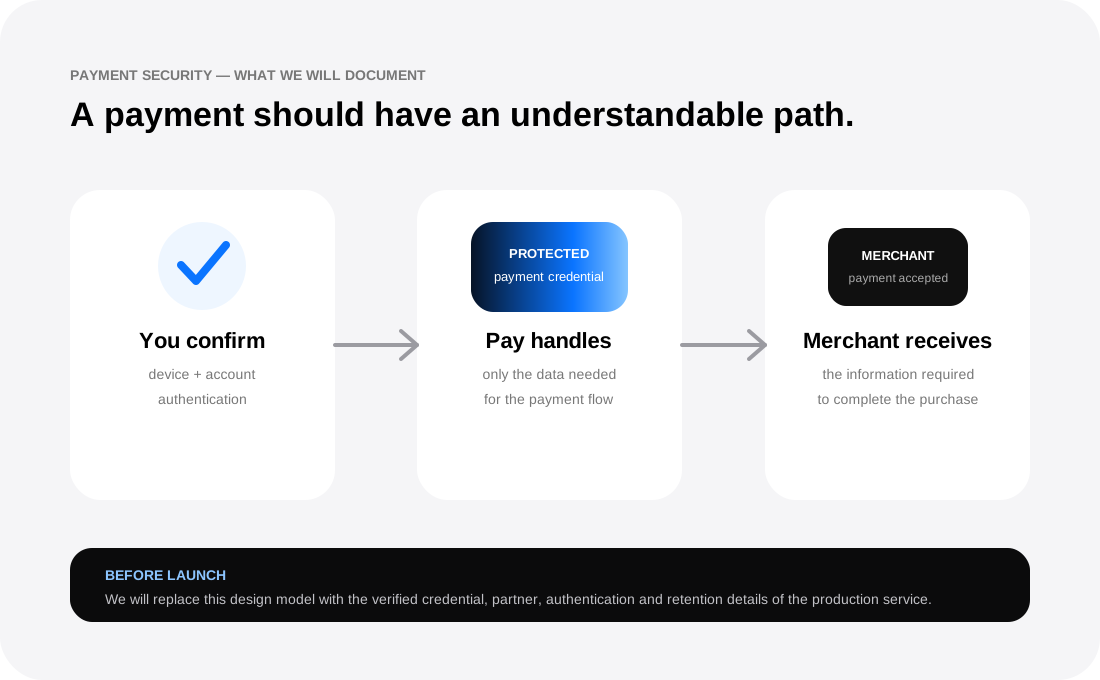
No vague security promises
Until the production architecture, payment partners, regulated roles, certifications and operational controls are confirmed, this site avoids claims such as “bank-grade,” “unhackable,” or “guaranteed fraud protection.”
What we intend to publish before payment launch
What happens to card or bank credentials and whether tokenized or network-provided credentials are used.
Exactly what a merchant receives to complete a payment and support the purchase.
Which regulated institutions and processors perform which parts of the payment flow.
Relevant compliance status, independent assessments and scope where publication is appropriate.
What payment information is retained, for how long and why.
How service incidents and material security events are communicated.
Authentication
Sensitive actions should require appropriate confirmation. The exact methods may vary by device and market and could include device authentication, eFind ONE account security, risk controls or additional verification required by partners or law.
At launch, this section will name the actual methods and explain when additional verification may be required.
Payment data and privacy
We want a customer to be able to answer five questions quickly: what eFind Pay sees, what a merchant sees, what a payment partner sees, what is stored, and whether payment information is used elsewhere in the eFind ecosystem.
The production privacy design and policy must match each other. Any statement about advertising or cross-service use should be published only when the technical and contractual controls support it.
Fraud, disputes and purchase problems
Before launch, eFind Pay will publish the exact process for unauthorized transactions, purchase disputes, refunds, mistaken transfers and account compromise. Protection can differ depending on the payment method, transaction type, partner and applicable law, so the interface should show the rule that actually applies.
Report a security issue
Security researchers or customers who believe they found a security issue can contact legal@efind.com during the pre-launch period. Before public payment launch, eFind Pay should publish a dedicated vulnerability disclosure process and security contact.
Trust principle
We would rather publish a precise limitation than a broad promise we cannot prove.